Proof-of-Reserves for a Tokenised GPU Credit Vault
Hardware attestation and market rates alone cannot prove a GPU vault is solvent.
Every serious PoR failure of the last three years shares one root cause: someone assumed a Merkle tree proves solvency by itself. It doesn't. A Merkle tree proves arithmetic. Whether the underlying assets are real, liquid, and worth what the report says they're worth is a separate question, one that exchange audits have mostly gotten away with dodging because a major cryptocurrency and USDT are fungible and trade on liquid markets. Tokenised GPU credit vaults don't get that shortcut. Their collateral is a rack of physical hardware sitting in a data center somewhere, and no block explorer on earth can tell you if it's turned on.
How leading exchanges implement PoR today, and where the bar sits
Kraken pioneered proof-of-reserves back in 2014 and now runs it quarterly alongside its regular financial disclosures. The March 2025 attestation showed the exchange holding 192,091.25 BTC against 167,188.68 BTC owed to customers, a 114.9% reserve ratio, while a prior attestation covered $21.5 billion in client assets. That liability count folds in margin, futures, and staked positions rather than just spot balances, which is a harder accounting problem than it sounds like on paper. An independent accountancy firm signs off on each round, and Kraken gives users a tool to check their own Merkle proof directly.
Binance took the mechanism further in February 2023, layering zk-SNARKs on top of its Merkle tree with Polyhedra Network. The zero-knowledge layer proves every customer balance got included and that no balance was negative, without revealing what any individual account actually holds. A plain Merkle proof can't give you that. It can only tell you the tree is internally consistent, which is a narrower guarantee than confirming the tree contains everyone.
The real story, though, is what these reports still can't reach. The Double-Helix Framework, published by Lazirko, Appelbaum, and Vasarhelyi in the British Accounting Review (available online August 2025), argues a complete crypto audit has to check on-chain, off-chain, and intersecting transactions all at once, going beyond just the on-chain strand a wallet signature makes easy to verify. Exchanges carry off-chain obligations no wallet attestation can reach, and that's already a known weak point in the model everyone's copying. For a GPU vault, where the entire asset base sits off-chain by definition, that weak point stops being a footnote and becomes the whole problem.
What a tokenised GPU credit vault actually is and why standard PoR does not transfer
A GPU RWA vault takes investor capital, buys or leases high-performance GPUs, puts them to work in data centers, and passes the resulting compute revenue back to token holders as yield. Compute Labs, a Solana-native protocol founded in early 2024 and based across Los Angeles and Seattle, is the most documented live example. Its Compute Tokenisation Protocol turns physical GPUs into GNFTs (GPU Non-Fungible Tokens) alongside a fungible miniGPU token, and its first vault, backed by NVIDIA H200 hardware running live AI workloads, launched with a $1 million initial deployment. Later vaults target B200 and GB200 (NVL) chips across Tier 3 and Tier 4 data centers, aiming for 30% to 70% APY. The pre-seed round in April 2024 raised $3 million at a $30 million fully diluted valuation, and was oversubscribed by 2x.
USD.AI runs a related but distinct model: a lending protocol collateralized by a specific asset type, where every USDai token is backed 1:1 by stablecoin reserves, and loans against that collateral make up close to half of total reserves alongside PYUSD and wrapped US T-Bills. It raised $13 million from Framework Ventures in August 2025 and has put out $225 million in loans against over $1.2 billion in approved facilities.
Here's the actual reason the exchange playbook breaks. Exchange PoR works because both sides of the ledger, the on-chain wallet and the customer balance, are fungible tokens the same blockchain can read. A GPU credit vault's reserve is a rack of hardware sitting off-chain, invisible to any explorer. Worse, the credit itself is non-fungible and time-bound: a scheduled hour of GPU compute for next Tuesday is not interchangeable with a scheduled hour three months out, and an idle GPU sitting in a rack is not the same reserve item as one running a training job at full load. Yield comes from usage, so proof-of-reserves has to attest to revenue-generating capacity, going beyond a headcount of chips sitting in a warehouse.
Attesting that the hardware exists and is operational (the asset side of GPU PoR)
Standard PoR asset attestation is almost boringly simple: sign a message from a wallet address, and the chain tells you whether the signer controls the funds. Deterministic, instant, no third party needed. GPU attestation needs three separate layers just to reach that same starting line, and skipping any one of them is where a vault operator can quietly cook the books.
Layer one is physical custody: documented legal title or lease terms tied to specific GPU serial numbers in a named facility, signed off by a third-party custodian. Layer two is operational status, proving the hardware is actually running rather than sitting racked and idle, which ownership paperwork alone can never show. Layer three is utilization and revenue, proving the hardware is generating the yield the vault promised its token holders. Most vaults today can produce layer one without much trouble. Layer three is where the claims get soft.
Hardware can close part of this gap on its own. NVIDIA's Confidential Computing on the Hopper accelerator puts a trusted execution environment (TEE) directly on the chip, anchored to keys fused in at manufacture, with secure boot verifying signed firmware and a host-side TEE checking the attestation reports. That's a real cryptographic root of trust, for a single chip. Current GPU confidential computing doesn't extend to multi-GPU workloads, though, and frontier training runs span hundreds or thousands of accelerators at once. Broader multi-GPU support is not production-ready today. So a TEE can vouch for one chip and stays silent about the cluster around it.
Compute Labs' operational approach targets real-time oversight of the physical GPU fleet, aiming to confirm hardware is verifiable on-chain, in working condition, and insured. Anyone doing real diligence should check a vault's claimed revenue against a market rate before trusting the yield number: a high-end NVIDIA GPU runs upward of $7.90 an hour on a legacy cloud provider, and a vault promising well above what that rate implies deserves a harder look.
One gap remains, and it is structural in nature. Operational dashboards are built and controlled by the vault operator itself, which means they carry exactly the counterparty trust risk proof-of-reserves was invented to remove in the first place. Self-reported uptime is not proof of uptime. That's what pushes the whole system toward an oracle layer.
Bridging off-chain hardware data to the chain (the oracle architecture)
GPU vault PoR splits cleanly into two halves. One half is on-chain, and anyone with a block explorer can check it. The other half is off-chain, and requires someone, or something, to be trusted. Nearly all the real risk in this model sits at the seam where those two halves meet, and that seam is exactly where most vaults will be tempted to cut corners.
Standard DeFi price oracles aren't built for this. A price feed for a liquid token can lean on a deep secondary market. A tokenized physical asset has no such market, so it needs off-chain appraisals, live operational metrics, and third-party valuation instead of a price tick.
Chainlink's proof-of-reserves product for real-world assets is the clearest existing template. Chainlink's decentralized oracle networks have secured over $14 trillion in cumulative transaction value across DeFi and institutional use, according to Chainlink Labs' 2025 figures. The PoR feed connects to a custodian or another off-chain data source, and if the reported reserve value drifts from what's minted on-chain, the oracle updates the attestation, which can trigger automated circuit breakers that pause minting or transfers once a vault falls under-collateralized.
For a GPU vault, that feed has to carry more than a dollar value: uptime percentage, jobs dispatched, revenue accrued per period, each one needing an authenticated source before any oracle network will take it in. USD.AI's approach, tracking its loan pipeline through a public Dune dashboard, shows real-time reporting on a mixed collateral pool is doable in practice, and not merely on paper.
Even the best decentralized oracle network is only as honest as whatever feeds it, though, and for GPU utilization that source is ultimately the data center operator's own monitoring API. That's the weak link nobody wants to name. Closing it for good means either an independent audit of that API or TEE-generated, signed telemetry feeding the oracle directly, and that piece of the stack isn't solved yet. Any vault that claims otherwise is asking for trust it hasn't earned.
Two depreciation problems that any GPU PoR must account for
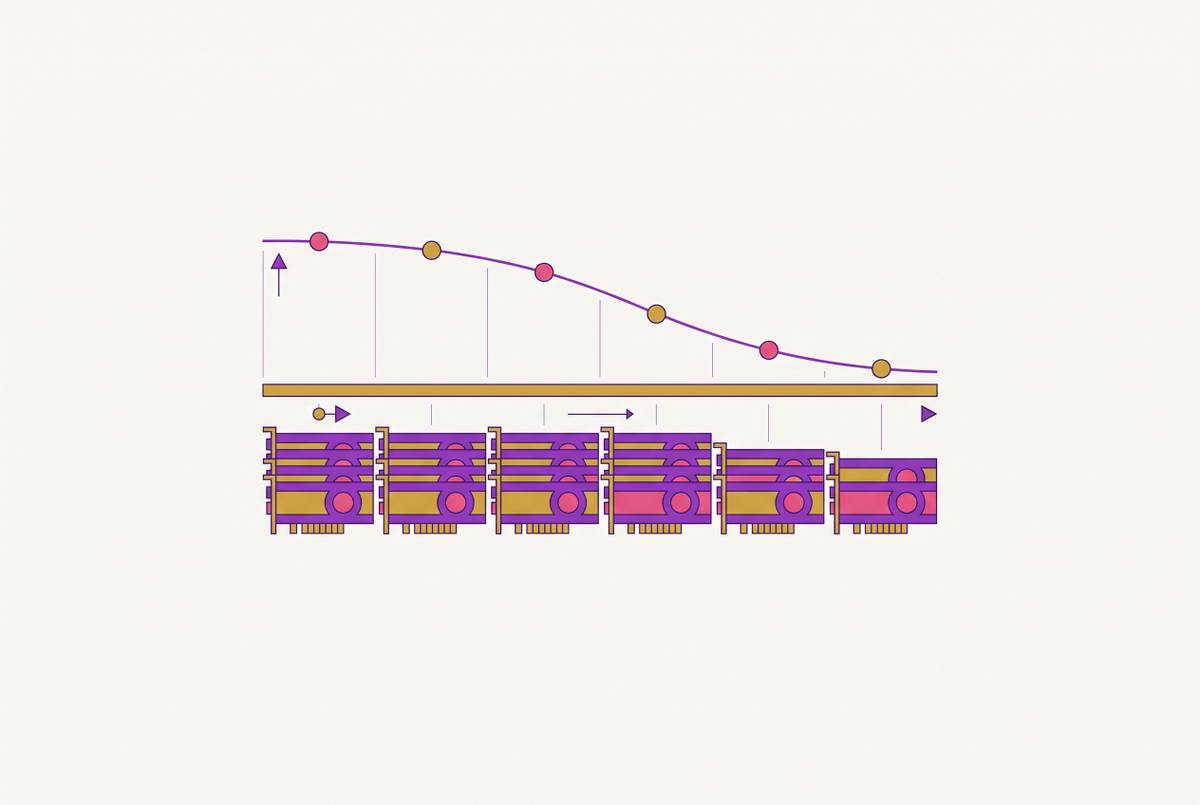
Gold doesn't depreciate. Treasuries don't depreciate. GPUs do, fast and unevenly, and this is where most GPU PoR proposals quietly fall apart. GPU generations have historically turned over in roughly one to two years, and as the market value of the underlying hardware falls, so does the value of the collateral backing the token, even when the unit count on the rack hasn't moved at all.
A point-in-time PoR that just counts GPU units, without marking them to current market value, overstates the reserve every single time. The attestation needs a net-asset-value figure built on depreciated hardware value, reflecting what the chips are worth right now rather than what the vault paid for them eighteen months ago.
A second pressure runs the same direction: rental rate compression. As the supply of H100 and H200-class hardware grows across the market, spot rental rates for that hardware fall, and a PoR that verifies a chip physically exists but says nothing about its current utilization or realized revenue isn't good enough for a credit vault whose entire pitch to investors is yield. Cadence matters too. Kraken runs PoR quarterly, but GPU hardware moves faster than exchange balance sheets do, so a GPU vault needs at least that frequency, arguably more, with quarterly serving as a floor.
This is where the asset side and the liability side of the proof stop being separate problems. If hardware NAV falls faster than the redemption claims sitting in outstanding tokens, the vault is insolvent, full stop, even if the PoR shows 100% of GPU units accounted for. The liability tree has to be computed against current hardware NAV. Computing it against original purchase cost isn't a rounding error, it's the whole vault lying to itself.
Building the liability side: Merkle-tree accounting for GPU credit token holders
In a standard exchange liability tree, every leaf is just a customer's balance in BTC or USDT, and leaves aggregate cleanly because every unit is identical to every other unit. A GPU credit vault's liability tree doesn't get that convenience. Each leaf represents a token holder's claim on a specific quantity of GPU-hours, and those claims stop being uniform the moment vaults get stratified by hardware generation, data center region, or rental tenure.
That forces real changes to the structure. Each Merkle leaf has to encode a full credit specification beyond just a quantity: hardware type, data center tier, delivery window, and the estimated utilization rate at the time of attestation. The root hash then represents total GPU-hour obligations denominated in current NAV, rather than a plain token count. An auditor still has to confirm the asset-side oracle feed, hardware NAV plus utilization, equals or exceeds that liability root. Structurally, that's the same test exchange PoR runs. The difference is that both sides of the equation are now moving targets instead of numbers that hold still.
The zk-SNARK layer matters more here than it does for an exchange. Binance's February 2023 implementation proved balance inclusion and non-negativity without exposing any individual holder's position. A GPU vault needs that proof to do one more thing: show that no single credit allocation gets double-counted across separate vaults or overlapping time periods, a risk that doesn't even exist when every unit is a fungible token. Done right, a zk-SNARK can prove the Merkle tree was built correctly over these heterogeneous, credit-denominated leaves, without revealing what any individual holder actually owns.
None of that closes the most basic failure mode. A custodian can quietly leave accounts out of the liability tree, understating what's actually owed, and the resulting Merkle proof stays mathematically valid the entire time, because the math was never the part that lied. This is exactly the structural warning the Double-Helix Framework raises: real verification has to span on-chain, off-chain, and intersecting transactions, with the degree of separation between ledgers made explicit. For a GPU vault, the attestation report itself has to itemize which obligations were checked purely on-chain, which needed authenticated off-chain data, and which needed both at once.
What a credible GPU credit vault PoR report must contain
Put the pieces together and a credible report takes a specific shape, and it looks nothing like a screenshot of a wallet balance. It needs documented physical custody down to GPU serial number, signed off by a third party rather than self-attested by the vault. It needs operational telemetry, uptime, jobs run, revenue realized, delivered through an oracle feed with an authenticated data source behind it, going beyond a dashboard the vault operator controls alone. It needs hardware marked to current NAV rather than acquisition cost, on a cadence tight enough to catch depreciation and rental-rate compression before either one does real damage.
It needs a liability-side Merkle tree built from heterogeneous, credit-denominated leaves, checked by an auditor whose scope explicitly covers completeness of inclusion as well as correctness of the hash tree. And the report itself has to say plainly which claims were verified on-chain, which relied on authenticated off-chain data, and which required both.
Exchange PoR set the expectation that solvency should be provable, and that expectation now attaches to GPU credit vaults whether their collateral cooperates or not. The hardware doesn't sit on a blockchain, it depreciates on a schedule nobody can pause, and its yield depends entirely on whether it's actually running a workload at the moment someone bothers to check. Meeting the bar exchanges set, with collateral this different, means solving each of these problems in the open. Assuming the old Merkle-tree template will stretch to fit something it was never built for is how the next $8 billion hole gets dug.